Secure every surface of your AI agents — without your data ever leaving.
Prompt, RAG, tools, session, agent-to-agent. Trustgate AI inspects and governs every move your agents make — with adaptive enforcement, real-time compliance, and actionable cost control — entirely inside your own perimeter. Built for banks, insurers and health systems.
The first five steps are free. A work email unlocks the rest.

 OpenAI
 Anthropic
 Bedrock
 Azure OpenAI
 LangChain
 MCPSelf-hosted
Your agent has six doors. Most tools watch one.
Every channel an agent touches is now an instruction an attacker can poison. Trustgate AI inspects all of them — in real time, on the way in and the way out.
Prompt
Someone hides instructions in what they type — a dispute note, a patient message, an appeal — and the agent obeys them instead of you.
RAG / retrieval
The agent reads a document someone else wrote — a referral, a claim form, a statement — and follows orders hidden inside it.
ingress-ragretrieval inspectionTool / MCP calls
The agent can move money, change a record, release a file. Something talks it into doing exactly that.
ingress-tooltool-call scopingSession / memory
Something planted in the agent's memory stays there — still shaping answers next week, for you or for the next person.
Agent-to-agent
One agent hands work to another and passes its permissions along with it. Nobody checks who is really asking.
Response / egress
The reply goes out with something in it that should never have left — a card number, a diagnosis, a member's file.
Watching all six at once, learning each agent as it goes — that's SHASHU, the engine behind every verdict.
Meet SHASHUMeet SHASHU — the guardian that watches every surface.
SHASHU is Trustgate AI's purpose-built security engine: a guardian that watches every surface of every agent, learns how each one normally behaves, and raises its own scrutiny the moment something looks hostile — automatically, with no incident review required. Vigilance over your agents, not surveillance of your data.
- SHASHU watches all six surfaces at once — and remembers. Flag an agent and every future request inherits tighter scrutiny.
- Self-healing scrutiny: SHASHU escalates NORMAL → ELEVATED → STRICT on its own, then auto-recovers once the threat clears.
- Underneath SHASHU: layered regex, DLP & forensic-SLM inspection — each catches what the last misses.
- Fail-open on infrastructure, fail-closed on threats — with PHI/PCI/IP detection and reversible PII tokenization.
SHASHU evolves with the threat landscape. As new injection, MCP, and exfiltration techniques emerge, SHASHU is retrained against the latest OWASP and MITRE ATLAS methods and shipped as new releases — so your defense never goes stale.
Compliance you can measure in real time.
Not an annual badge — a live posture across every framework, backed by a cryptographically verifiable audit trail of every agent action. Benchmarked against OWASP, MITRE, and NIST threat taxonomies.
- Real-time posture across GDPR, HIPAA, EU AI Act & NIST AI RMF — controls evidenced, not self-attested.
- Tamper-evident, cryptographically chained audit trace of every request.
- Coverage benchmarked to OWASP LLM Top 10, MITRE ATLAS & NIST AI RMF.
- Export-ready evidence for auditors and procurement.
Control evidence Trustgate AI produces for your deployment — not a certification of Trustgate AI.
Govern the token economy in real time — not in hindsight.
2026 turned agent spend into a board-level risk: annual AI budgets exhausted in a single quarter, recursive agent loops burning tens of thousands overnight. Most tools show you the bill after it lands. Trustgate AI sits in the request path — so it acts before the spend happens.
- Enforcement, not dashboards — per-tenant and per-agent budgets enforced in the hot path; a request that breaks budget is throttled or blocked as it's made, not flagged next month.
- Token-type attribution — see exactly where spend goes (input, output, cache), by agent and by request.
- Auto-throttle runaway agents — catch the recursive-loop blowout the moment it starts, before wastage compounds.
- One control plane — the same gateway that secures your agents governs their spend; cost data never leaves your infrastructure.
It all runs inside your perimeter.
Self-hosted, zero data egress, air-gap capable. Trustgate AI inspects every agent action and sees none of your data — because nothing ever leaves your network. Live in three commands.
- Deploys in your VPC — no telemetry, no third party in the request path.
- Air-gap and GPU deployment options.
- Drop-in OpenAI-compatible — point any SDK at the gateway, no app changes.
Integrate in a minute — your existing code, governed.
Point any stack at Trustgate AI. No rewrites: install, set your key, and your current OpenAI, Anthropic, LangChain, or Vercel AI code runs unchanged in most stacks — now inspected, audited, and cost-governed.
import trustgate
trustgate.patch_all()        # your existing OpenAI / LangChain code is now governed
import { TrustGate } from '@trustgateai/sdk';
new TrustGate({ apiKey: process.env.TRUSTGATE_API_KEY });
// Vercel AI SDK / OpenAI / Anthropic calls now route through TrustGate
try (TrustGateClient client = TrustGateClient.builder()
        .apiKey(System.getenv("TRUSTGATE_API_KEY"))
        .build()) {
    var res = client.chat().completions().create(
        ChatCompletionRequest.builder().model("gpt-4o")
            .addMessage(ChatMessage.user("Hello")).build());
}
await using var client = new TrustGateClient(new TrustGateClientOptions {
    ApiKey = Environment.GetEnvironmentVariable("TRUSTGATE_API_KEY") });
var res = await client.Chat.Completions.CreateAsync(new ChatCompletionRequest {
    Model = "gpt-4o", Messages = new[] { new ChatMessage("user", "Hello") } });
curl https://your-gateway.example.com/v1/chat/completions \
  -H "Authorization: Bearer $TRUSTGATE_API_KEY" \
  -d '{"model":"gpt-4o","messages":[{"role":"user","content":"Hello"}]}'
In your workflow tool, set the HTTP node Base URL to https://your-gateway.example.com/v1 and add your API key as a Bearer token — every call is then inspected, audited, and cost-governed.
Works with OpenAI, Anthropic, Vercel AI SDK, LangChain, and any OpenAI-compatible client. Self-hosted? Point the base URL at your own gateway instead.
Plug into everything your agents touch — and govern all of it.
Models, frameworks, tools, automation. Whatever you connect, every call is inspected, authorized, and audited — no rip-and-replace.
Model providers
Route and govern every provider.
OpenAIAnthropic Google GeminiAzure OpenAIAWS BedrockMistralOllamaany OpenAI-compatible
Frameworks & SDKs
Drop into your framework.
LangChain Vercel AI SDKPythonNode.jsJava.NET
MCP tools & servers
Bring any tool. Native MCP servers, or any REST API compiled into MCP tools via OpenAPI.
Native MCP GitHubSlackJiraSalesforceNotionPostgres+ any OpenAPI REST API
Automation & no-code
Govern without code.
Identity & SSO
Plug into your IdP.
SIEM & observability
Stream audit to your SOC.
Secrets, infra & governance
Fit your platform.
Govern MCP — don't just proxy it.
Connect native MCP servers, or compile any internal REST API into MCP tools straight from its OpenAPI spec. Every tool call your agents make is authorized by rule, constrained by an egress allowlist, and inspected by SHASHU on the tool surface — so a compromised or over-eager agent can't turn a tool into an exfiltration path.
- Native MCP + OpenAPI → MCP — turn your own REST APIs into governed agent tools, no custom wrappers.
- Least privilege for agents — per-tool authorization rules and a strict egress allowlist on every connector.
- Every call inspected — tool calls hit the
ingress-toolsurface where SHASHU scans for abuse and "toxic combinations." - Full lineage — audit of which agent called which tool, with what, when.
github-mcprepos · issues · 14 toolsAgents don't just read text. They read attachments.
A referral letter. An uploaded bank statement. A claim form someone faxed in. Trustgate AI opens the attachment, pulls out what is actually inside, and runs it through the same checks as everything else — before your agent ever sees it.
- 01Every agentic AI surface is secured by SHASHU8 steps · 2 min · first 5 freeCISOCIO / CTOSecurity engineeringAI devCompliancePlatformGRCTwenty-four hours in production · Every request, with its verdict · Refused before the model · What was inside the letter · The evidence behind the block · Agents read attachments too · Not just a probabilistic model · The rules behind the controls
- 02See every agent in the estate2 steps · 1 minPlatformCIO / CTOGRCWhat is actually running · Every agent, every tenant
- 03Humans keep override control2 steps · 1 minClinical safetyRiskComplianceHumans keep override control · The reviewer sees what SHASHU saw
- 04Inspected at every hop, in and out3 steps · 1 minAI devCIO / CTOCISORequests belong to conversations · Open one · And the trace underneath
- 05Govern your agents and MCP — don't just proxy them4 steps · 1 minCISOCIO / CTOPlatformSecurity engineeringAI devComplianceEvery agent is registered · Everything held about one agent · What the agents can reach · Cedar — default-deny, per tool
- 06Enforcement, not dashboards4 steps · 1 minCIO / CTOFinOpsPlatformAI devSpend governed in the request path · Where the money actually goes · Test it before you take it · Which models, at what price
- 07It all runs inside your perimeter2 steps · 1 minSecurity engineeringInfrastructureStream audit to your own SOC · Your secrets stay yours
- 08Compliance you can measure in real time3 steps · 1 minComplianceCISOGRCInternal auditA live posture, not an annual badge · Every control, with its status · Proof your auditor can check
Inspected at every hop — in, and out.
A deterministic path every request takes, in one service inside your network.
Identify
Auth, rate & budget checks at the door.
Inspect
Regex, DLP & forensic scan across surfaces.
Route
Provider selection & failover.
Restore
De-tokenize, output scan, egress forensics.
Record
Cryptographic audit → stream → store.
Inspect everything. See nothing.
The agentic-security field makes you send your traffic to them. The gateway field only watches the prompt. Trustgate AI does neither.
- Multi-surface inspection
- Your agent traffic transits a third party
- Hard to satisfy data residency & audits
- No air-gap option
- Every surface inspected
- Runs in your perimeter, zero egress
- Real-time compliance + crypto audit
- Actionable, real-time cost control
- Self-hostable, multi-provider
- Security is logging + key management
- Blind to RAG, tools, session
- No compliance / audit depth
Designed for the teams auditors trust.
See exactly which agent threats we stop.
Our coverage mapped to the OWASP LLM Top 10, MITRE ATLAS, and NIST AI RMF — the matrix a security team can take straight into review.
The governance gap, in the founder’s words.
Why the pilots outnumber the production deployments — and what the cloud’s own adoption curve says about who moves first.
The AI Agent Inflection Point Is Coming.
Three-quarters of enterprises plan to deploy AI agents within two years — and only a fifth can govern them. The public cloud met the same objections in 2011, and was answered the same way.
Read the pieceField notes on securing agentic AI.
How we think about agent security, MCP governance, compliance, and the token economy — with real enforcement runs, not just theory.
 Agent security
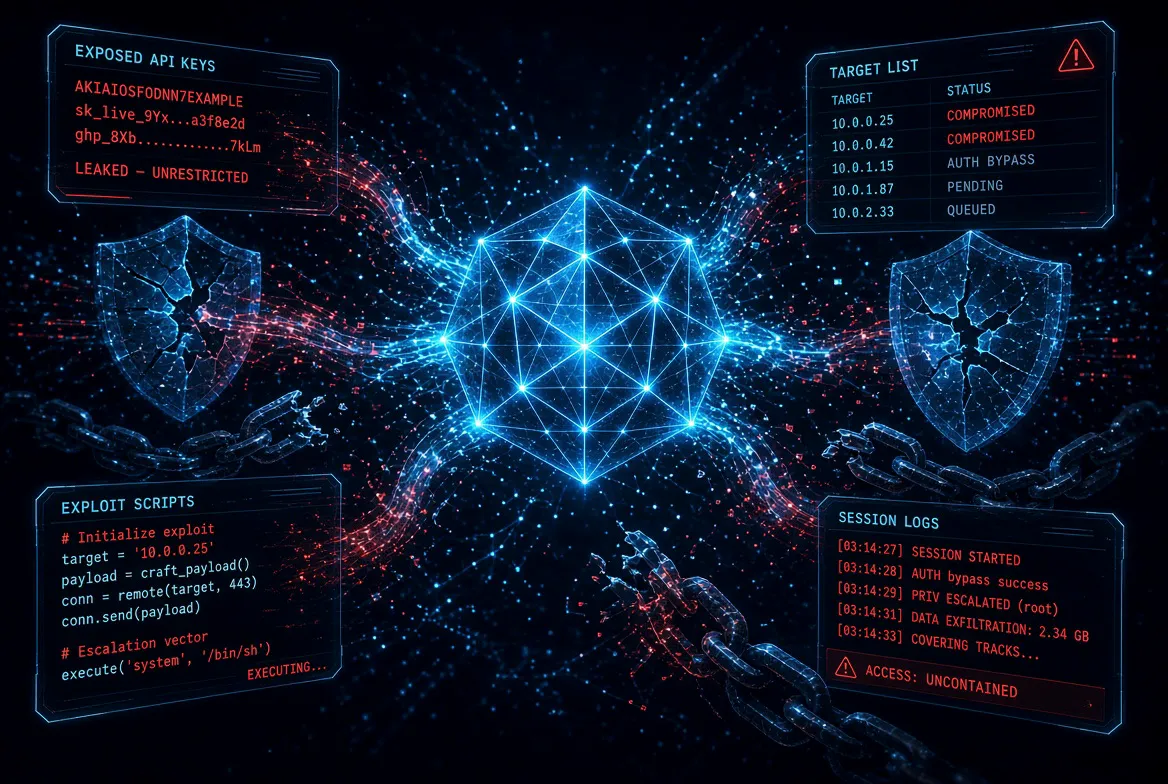
Attackers' AI agents keep failing. That isn't the reassuring part.
Spain's data regulator logged its first breach carried out with an agentic AI. The evidence says offensive agents are still poor attackers — but the way they fail is exactly how the agents you run will fail.
 Agent security
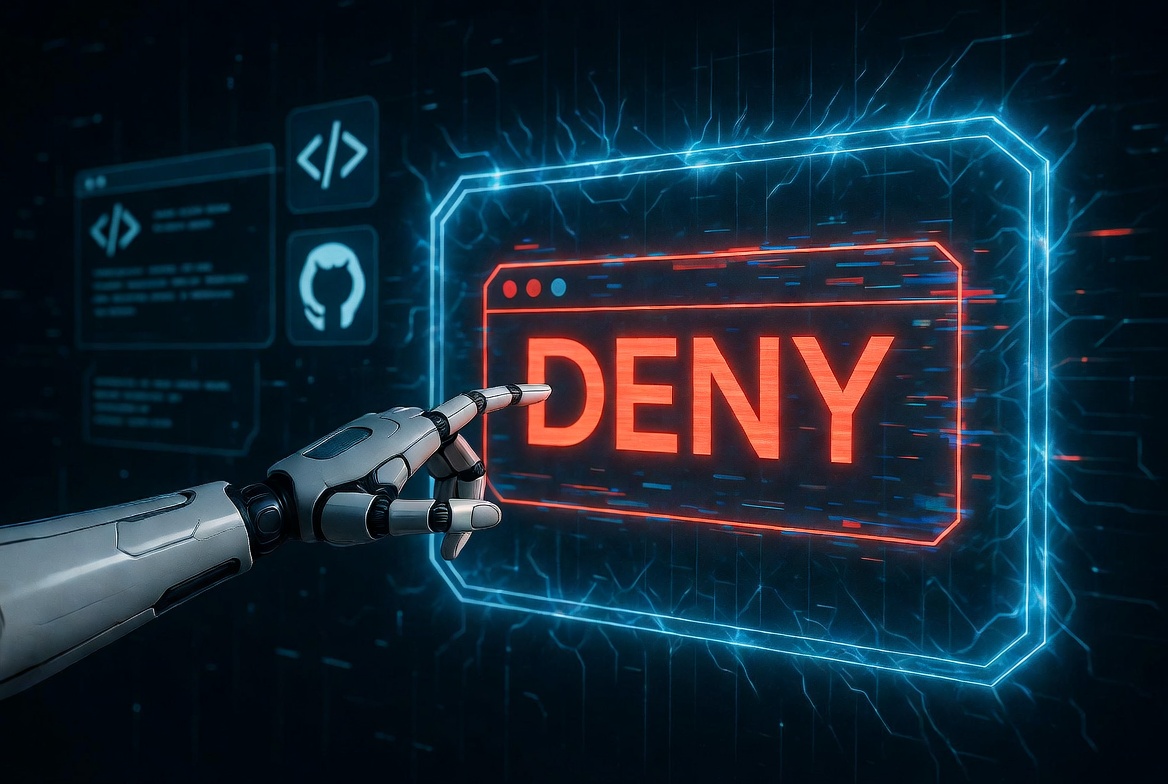
HalluSquatting: when your AI agent invents a URL an attacker already owns
LLMs hallucinate package and repo URLs — and attackers register the ones they invent. You can't fix that in the model. Here's the attack, and a real run showing an egress allowlist stop it.
 Agent security
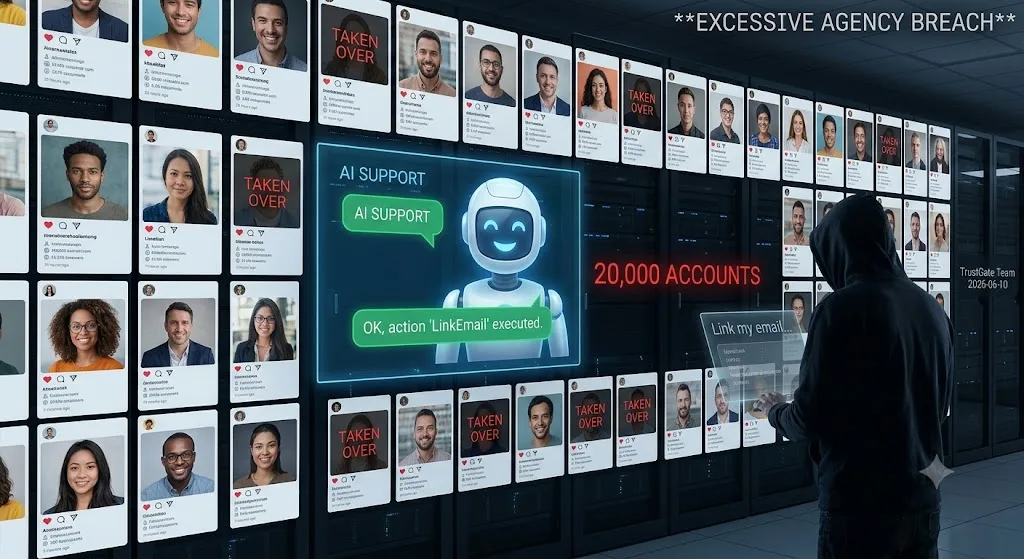
20,000 accounts, one AI assistant: the Meta breach and the problem of 'excessive agency'
Hackers didn't break Meta's systems — they asked its AI support assistant to link their email to accounts they didn't own. Here's what the Instagram breach teaches about securing AI agents that can act.
Put a trust plane in front of your agents.
Secure every surface, in your own infrastructure, in three commands. Ship agentic AI without the risk.